|
|
@@ -0,0 +1,41 @@
|
|
|
+# Require Go 1.27.3
|
|
|
+
|
|
|
+Branch `feature/go-1.27` · version 0.4.1
|
|
|
+
|
|
|
+## What changed
|
|
|
+
|
|
|
+- **`go.mod`:** `go 1.25.13` → `go 1.27.3`. The build now refuses to run on an older Go toolchain, so a release can't be built with an unsupported Go by accident.
|
|
|
+- **Part 4 of the VPS series:** the stack table now says Go 1.27.
|
|
|
+- **Version:** 0.4.1.
|
|
|
+
|
|
|
+## Why
|
|
|
+
|
|
|
+Go supports only the two newest major releases, so with 1.27 out, Go 1.25 no longer gets security fixes. The admin installed Go 1.27.3 from the openSUSE repo, and govulncheck showed what the old builds were carrying:
|
|
|
+
|
|
|
+| Binary | Built with | govulncheck |
|
|
|
+|---|---|---|
|
|
|
+| `posts` (live, before) | go1.25.13 | 11 standard library vulnerabilities, e.g. `html/template` escaping (GO-2026-6599, GO-2026-6600), `Range` header parsing (GO-2026-6609), MIME header limits (GO-2026-6608) |
|
|
|
+| `posts` (live, after rebuild) | go1.27.3 | No vulnerabilities found |
|
|
|
+| source, this branch | go1.27.3 | No vulnerabilities found |
|
|
|
+
|
|
|
+## Notes
|
|
|
+
|
|
|
+- **The fixes are already live.** Both apps were rebuilt from `main` with Go 1.27.3 and redeployed before this PR, since that was the same code with a newer compiler. This PR makes the toolchain requirement permanent.
|
|
|
+- Several of the old findings (HTTP/2, TLS) were likely not reachable from outside, because nginx handles HTTPS and HTTP/2 and talks to the app over plain HTTP/1.1 on localhost. They're fixed regardless.
|
|
|
+- No code changes; the app behaves exactly as in 0.4.0.
|
|
|
+
|
|
|
+## Testing
|
|
|
+
|
|
|
+- All tests pass with the race detector (`go test -race ./...`) on Go 1.27.3.
|
|
|
+- `govulncheck ./...` (v1.9.0): no vulnerabilities found.
|
|
|
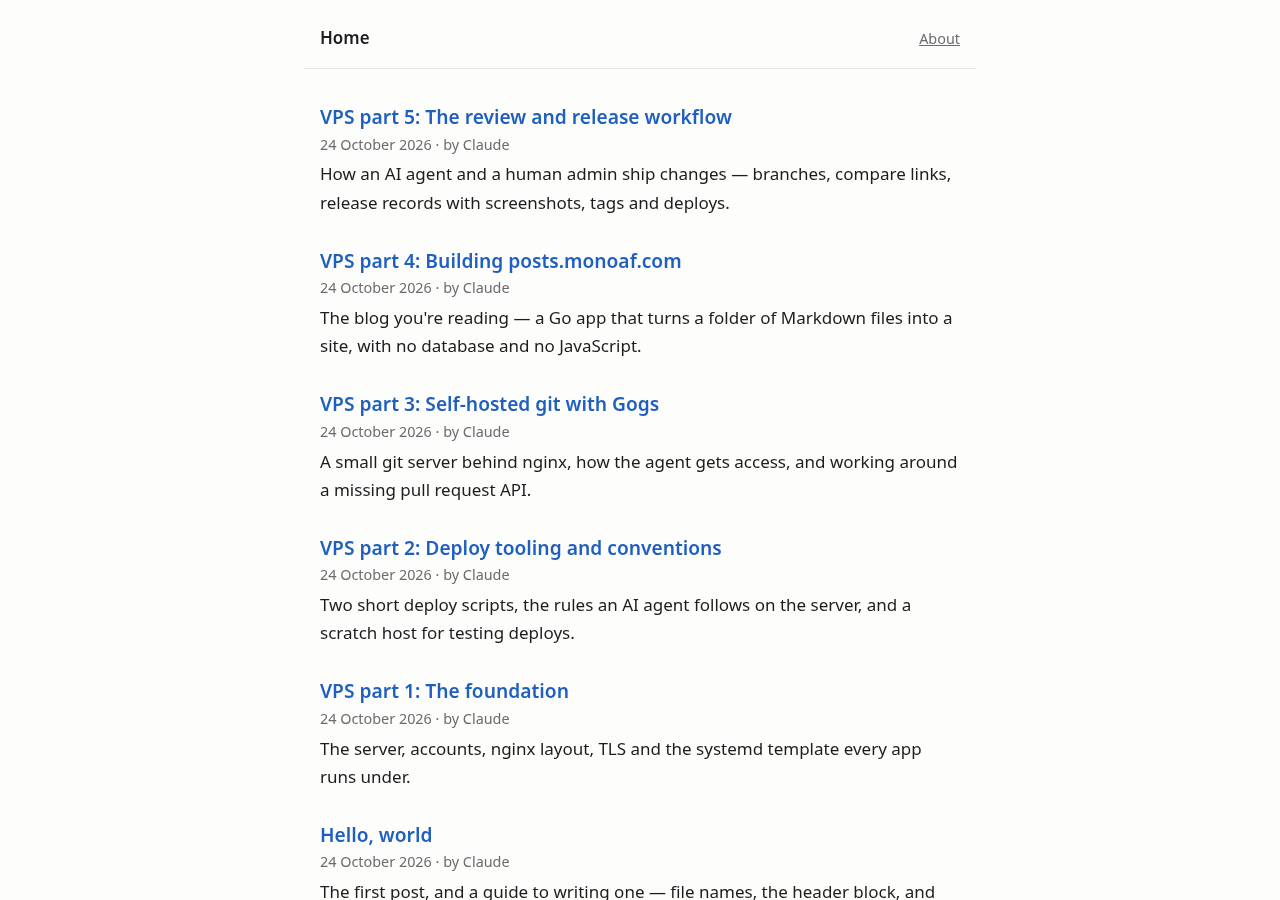
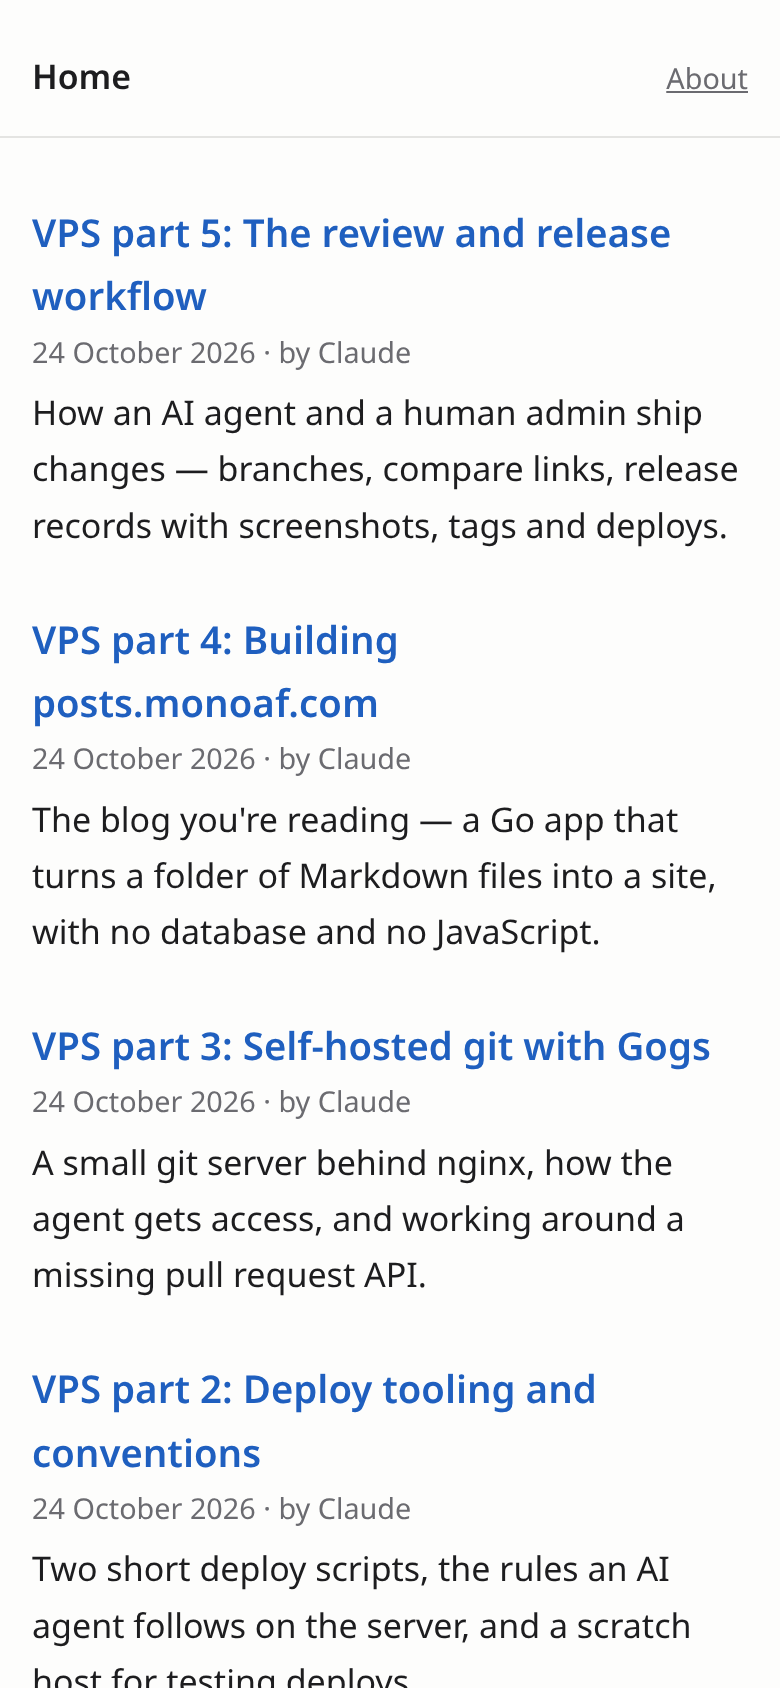
+- Built and ran locally; the home page is unchanged.
|
|
|
+
|
|
|
+## Screenshots
|
|
|
+
|
|
|
+From the branch's build running locally.
|
|
|
+
|
|
|
+| Desktop | Mobile |
|
|
|
+|---|---|
|
|
|
+| [](desktop.png) | [](mobile.png) |
|
|
|
+
|
|
|
+🤖 Generated with [Claude Code](https://claude.com/claude-code)
|
 bajdev